[DIGEST: CNN, The Guardian]
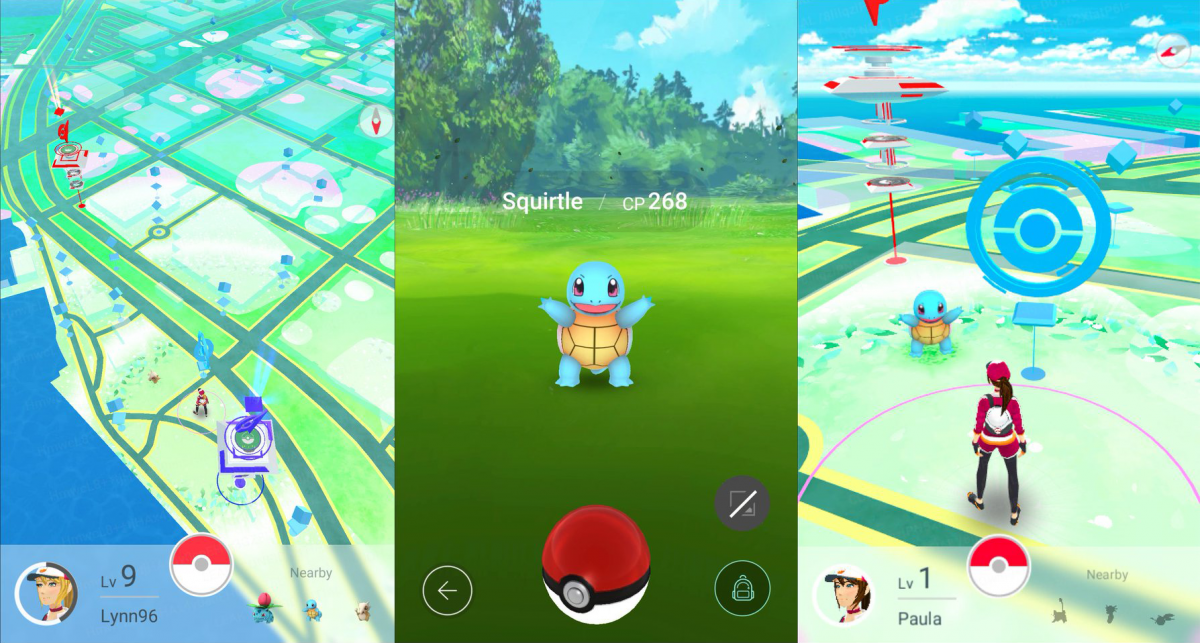
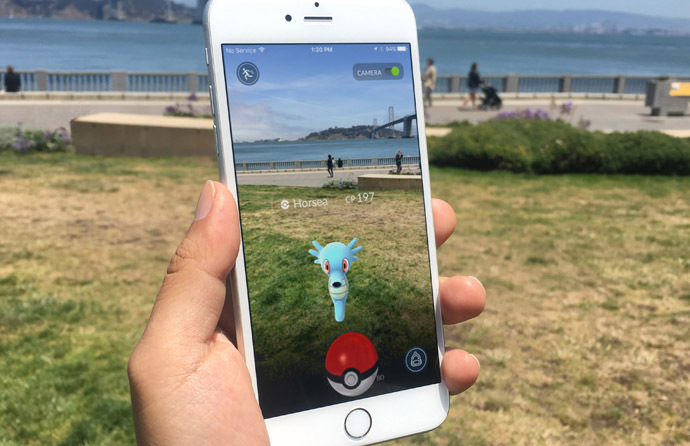
Niantic Labs, the developers of augmented reality game Pokemon Go, made emergency fixes to the game after discovering the app inadvertently had been granted full access to users’ Google accounts. The permissions appeared to affect players who signed up with their Google accounts on Apple devices. According to Google, “full access” means Pokemon Go "can see and modify nearly all information in your Google Account." This includes access to email. Nintendo of America, which owns the Pokemon brand, declined comment. Pokemon Go’s release last Thursday shattered industry records and sent Nintendo’s stock soaring. To date, the game has been downloaded on Android and Apple devices more than 5 million times.
The news sparked fears that playing the game would allow its developers to not only read and send email, but edit and delete documents in Google Drive and Google Photos and access individual browser and map histories. In a statement Monday night, Niantic assured users it only sought minimal information, specifically a user’s unique player ID and email address and that it was working to reduce the user permissions required to play the smartphone game. The company admitted, however, that “the Pokemon Go account creation process on iOS erroneously requests full access."
 Credit: Source.
It does not appear Niantic intentionally sought access to users’ personal data––Ingress, Niantic’s other augmented reality game, only requests minimal information from its users––but the company uses an outdated version of Google’s shared sign-on service. This approach is favored by app developers because it makes sign-up quicker and easier for players. It negates the need to create another online account using credentials already stored on their phones. Ideally, shared sign-ons should ask the user what permissions they want to grant the app. In this case, the permission-granting step was skipped because Niantic used an unsupported and out-of-date version of the sign-on process. This error then prompted Google to default to warning users that Pokemon Go had “full access” to their accounts.
It is difficult to ascertain just how much of the blame for the security scare can be apportioned between both parties, but it appears Google may have presented
the limited permissions granted as full access. “Once we became aware of this error, we began working on a client-side fix to request permission for only basic Google profile information, in line with the data that we actually access,” Niantic said. “Google has verified that no other information has been received or accessed by Pokémon Go or Niantic. Google will soon reduce Pokémon Go’s permission to only the basic profile data that Pokémon Go needs, and users do not need to take any actions themselves.”
Adam Reeve, a computer security expert at cybersecurity firm RedOwl, claimed he discovered the security vulnerability. In a blog post written Monday, Reeve said, "This is probably just the result of epic carelessness. I don't know how well they will guard this awesome new power they've granted themselves... I really wish I could play, it looks like great fun, but there's no way it's worth the risk." Mark Nunnikhoven, a computer security expert with cyber security firm Trend Micro, echoed Reeve’s concerns. "A game shouldn't require this amount of access to your data,” he said.
 Credit: Source.
However, fellow cyber security expert and Trail of Bits CEO Dan Guido cast doubt on Reeve’s claim after reaching out to Google tech support. Google assured him that “full account access” does not mean a third party can read or send email, let alone access files. In a statement, Google said that “In this case, we checked that the Full account access permission refers to most of the My account settings. Specific actions such as sending emails, modifying folders, etc, require explicit permissions to that service (the permission will say "Has access to Gmail").” Reeve has since backtracked on his claim, saying he wasn’t “100 percent sure” his blog post was true. Reeve, a former senior engineering manager at Tumblr, admitted he had never built an application that uses Google account permissions and had never tested the claims he makes in his blog post.
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 @stephaniematto/TikTok
 u/pineapplefountainz/Reddit
 u/CheckOk2685/Reddit
 u/dtaymanesq/Reddit
 u/sixth_hokage06/Reddit
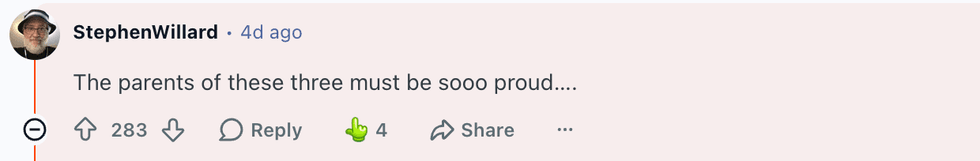 u/StephenWillard/Reddit
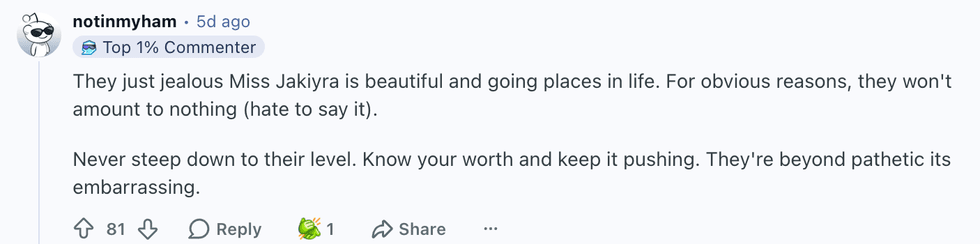 u/notinmyham/Reddit
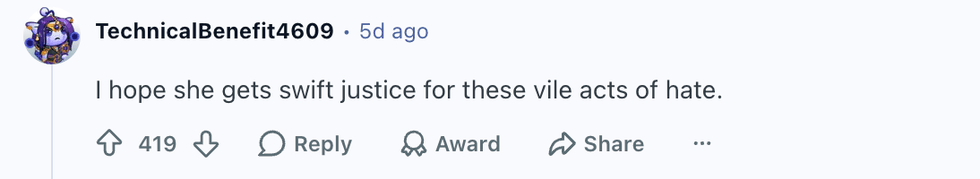 u/TechnicalBenefit4609/Reddit
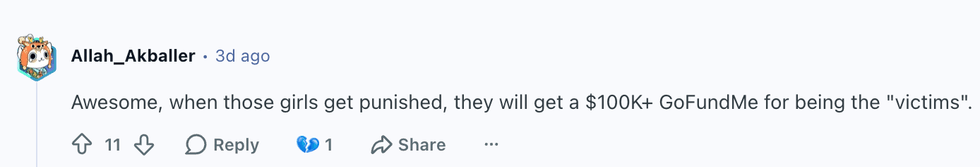 u/Allah_Akballer/Reddit
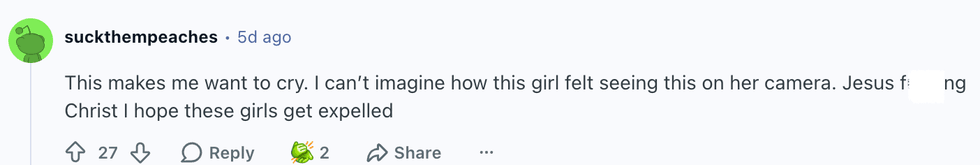 u/suckthempeaches/Reddit
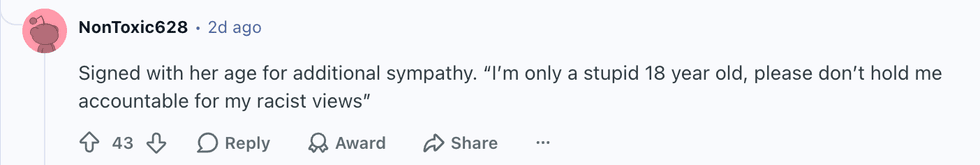 u/NonToxic628/Reddit
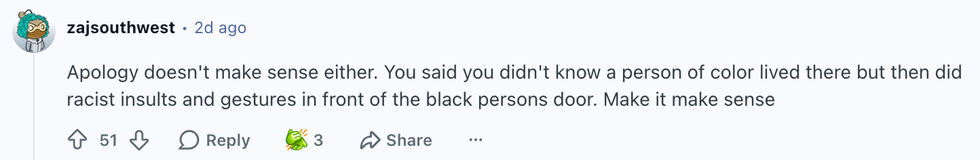 u/zajsouthwest/Reddit
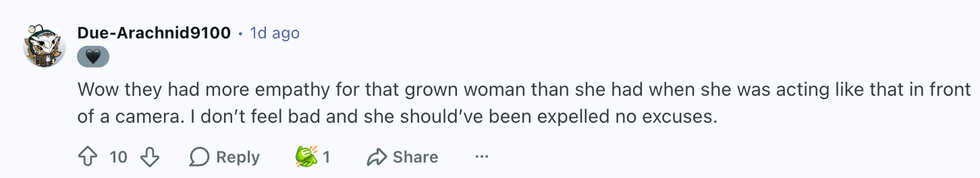 u/Due-Arachnid9100


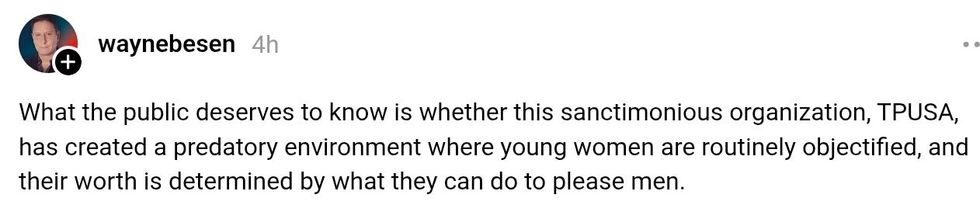 @waynebesen/Threads
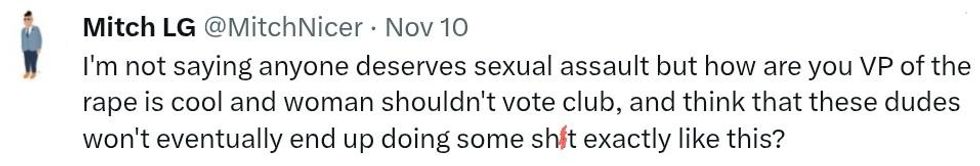 @MitchNicer/X
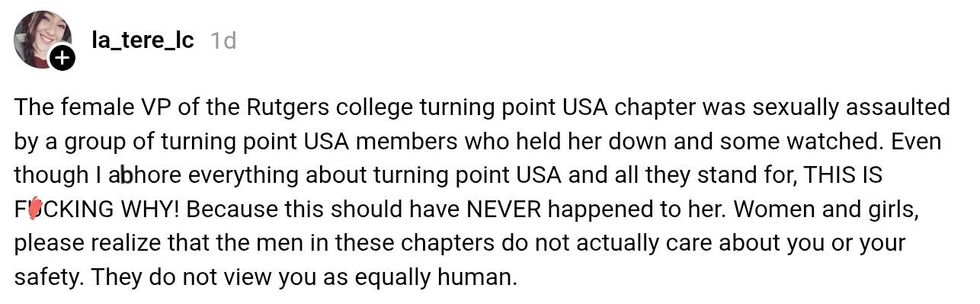 @la_tere_lc/Threads
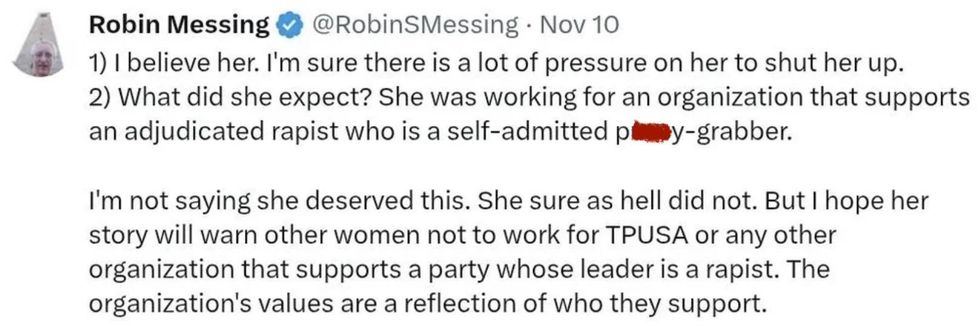 @RobinSMessing/X
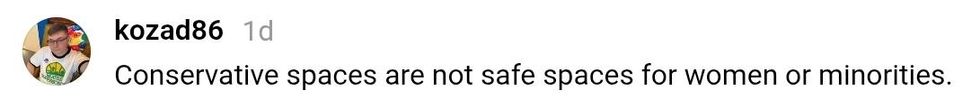 @kozad86/Threads
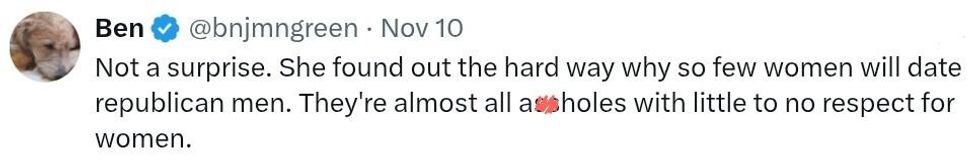 @bnjmngreen/X